Mobile Banking Security

FRAUD, MALWARE, AND BOTS

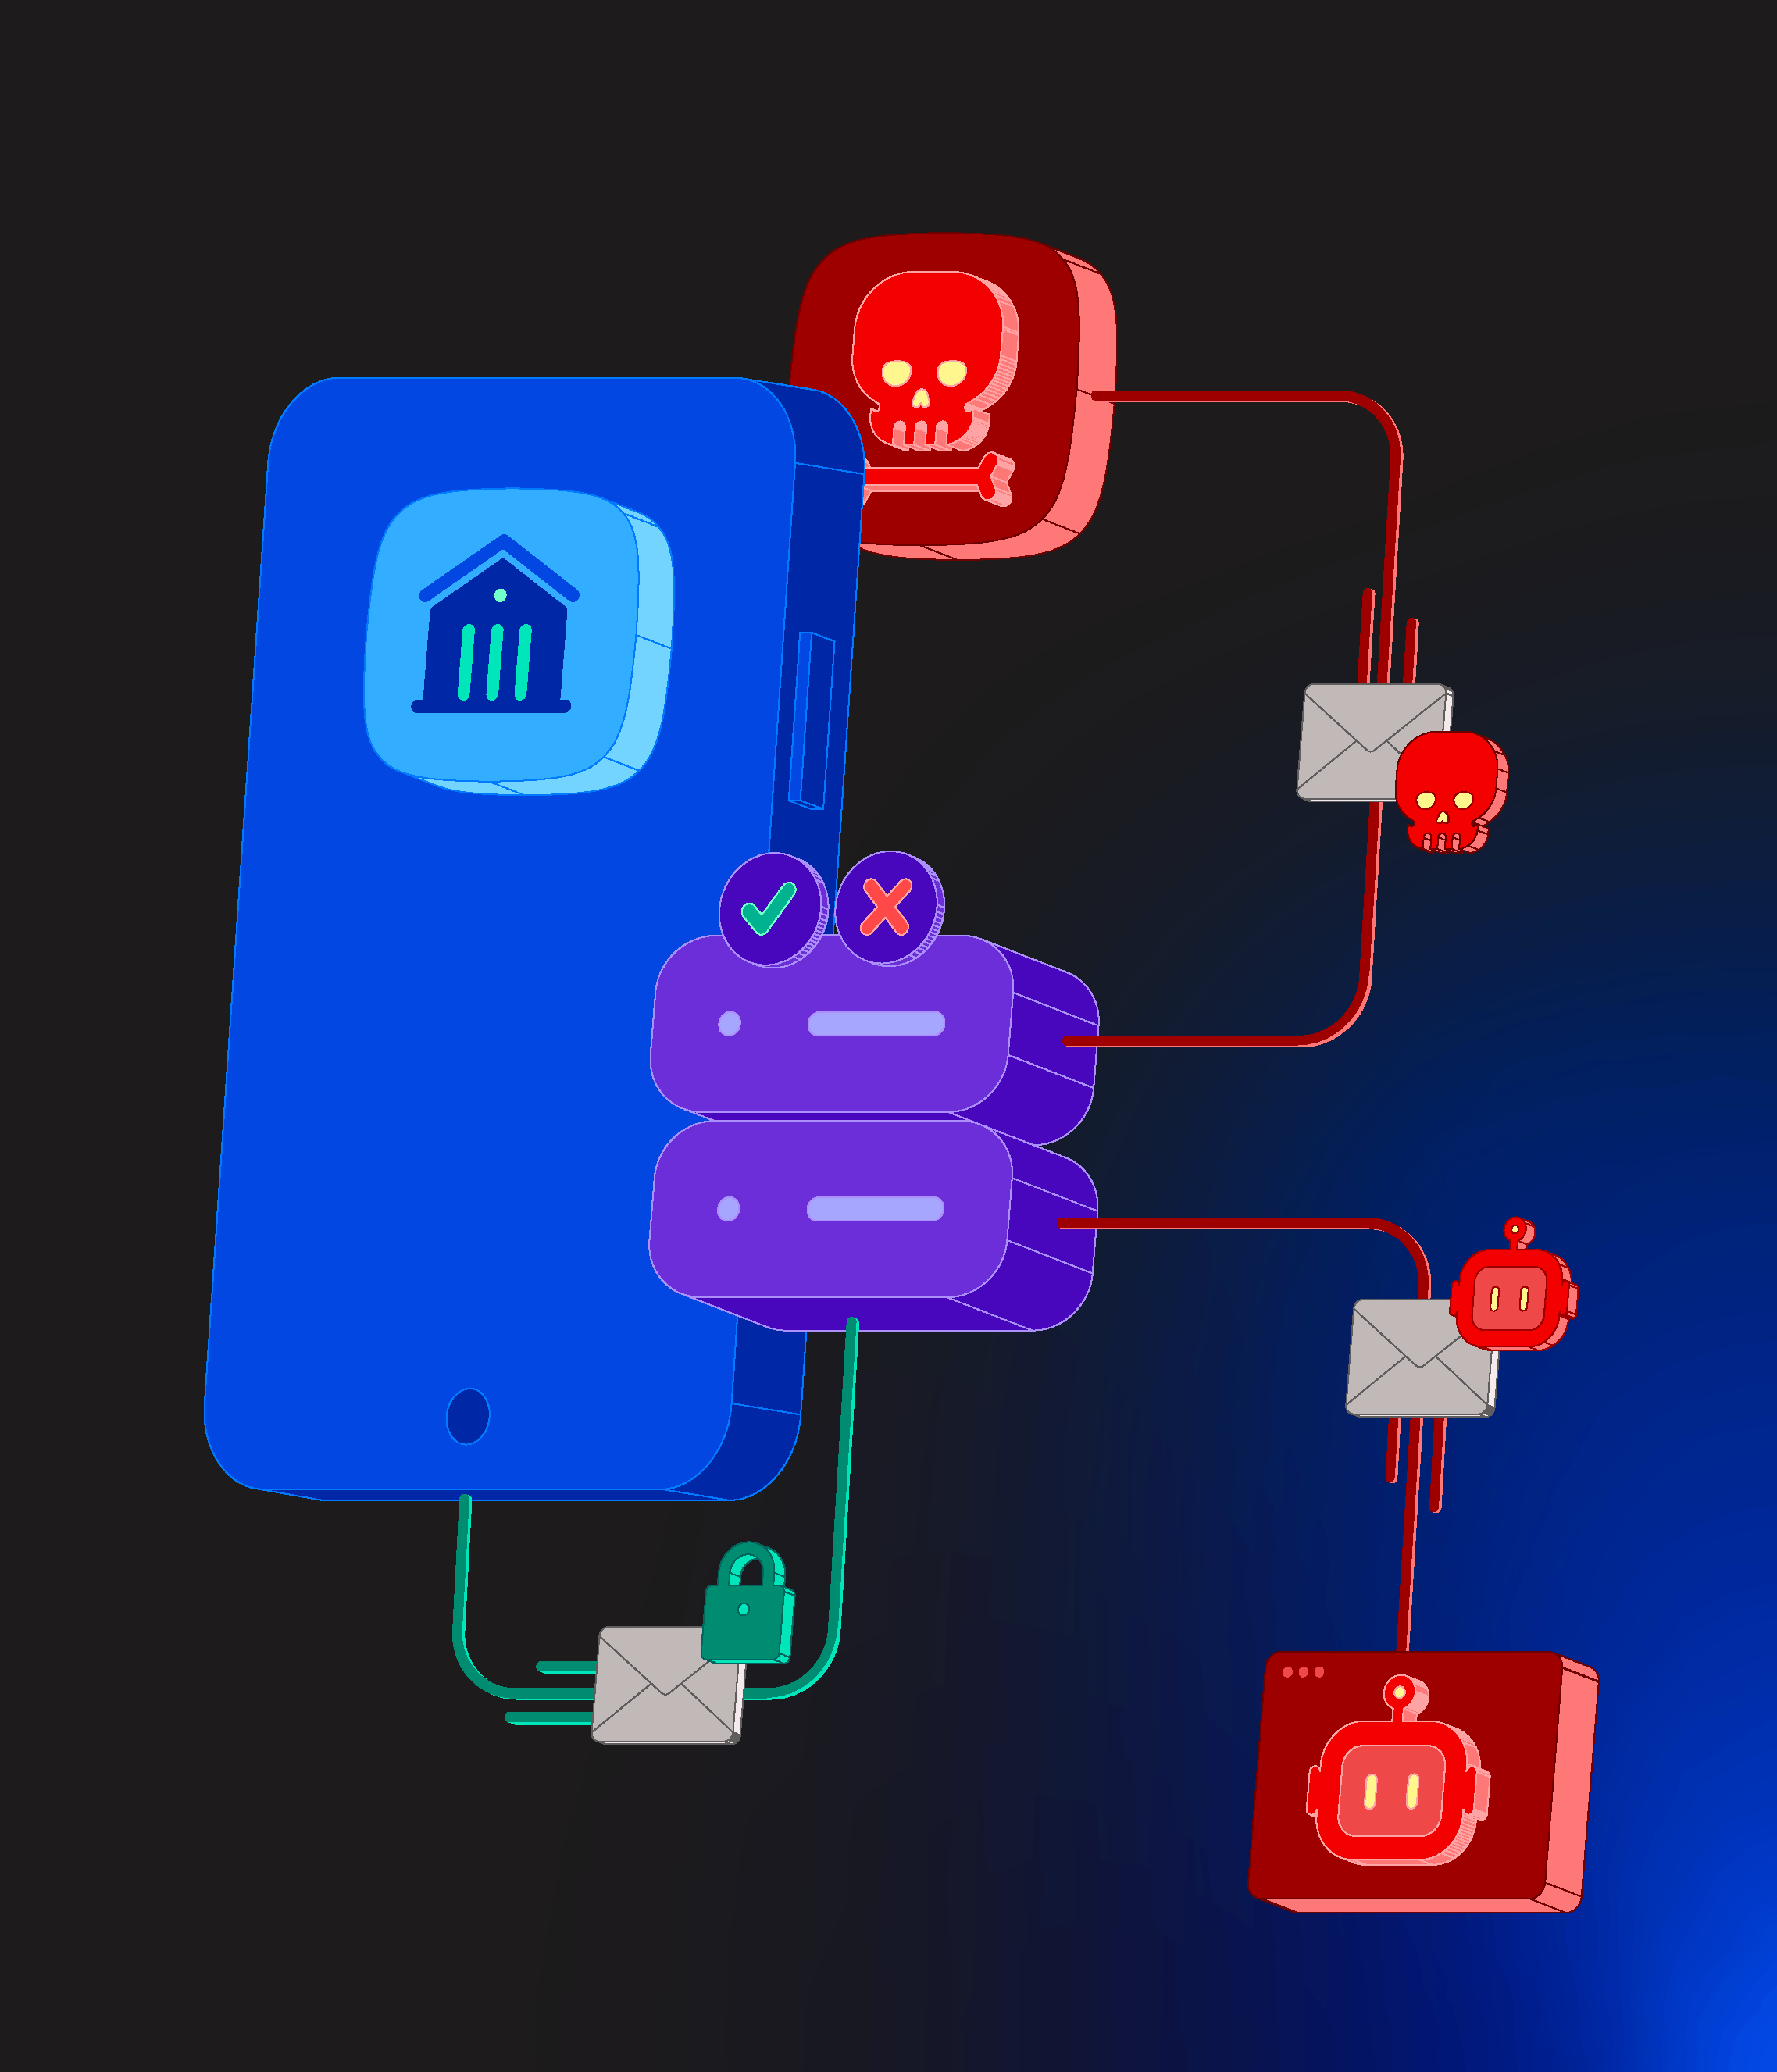
Mobile banking apps operate in zero-trust environments

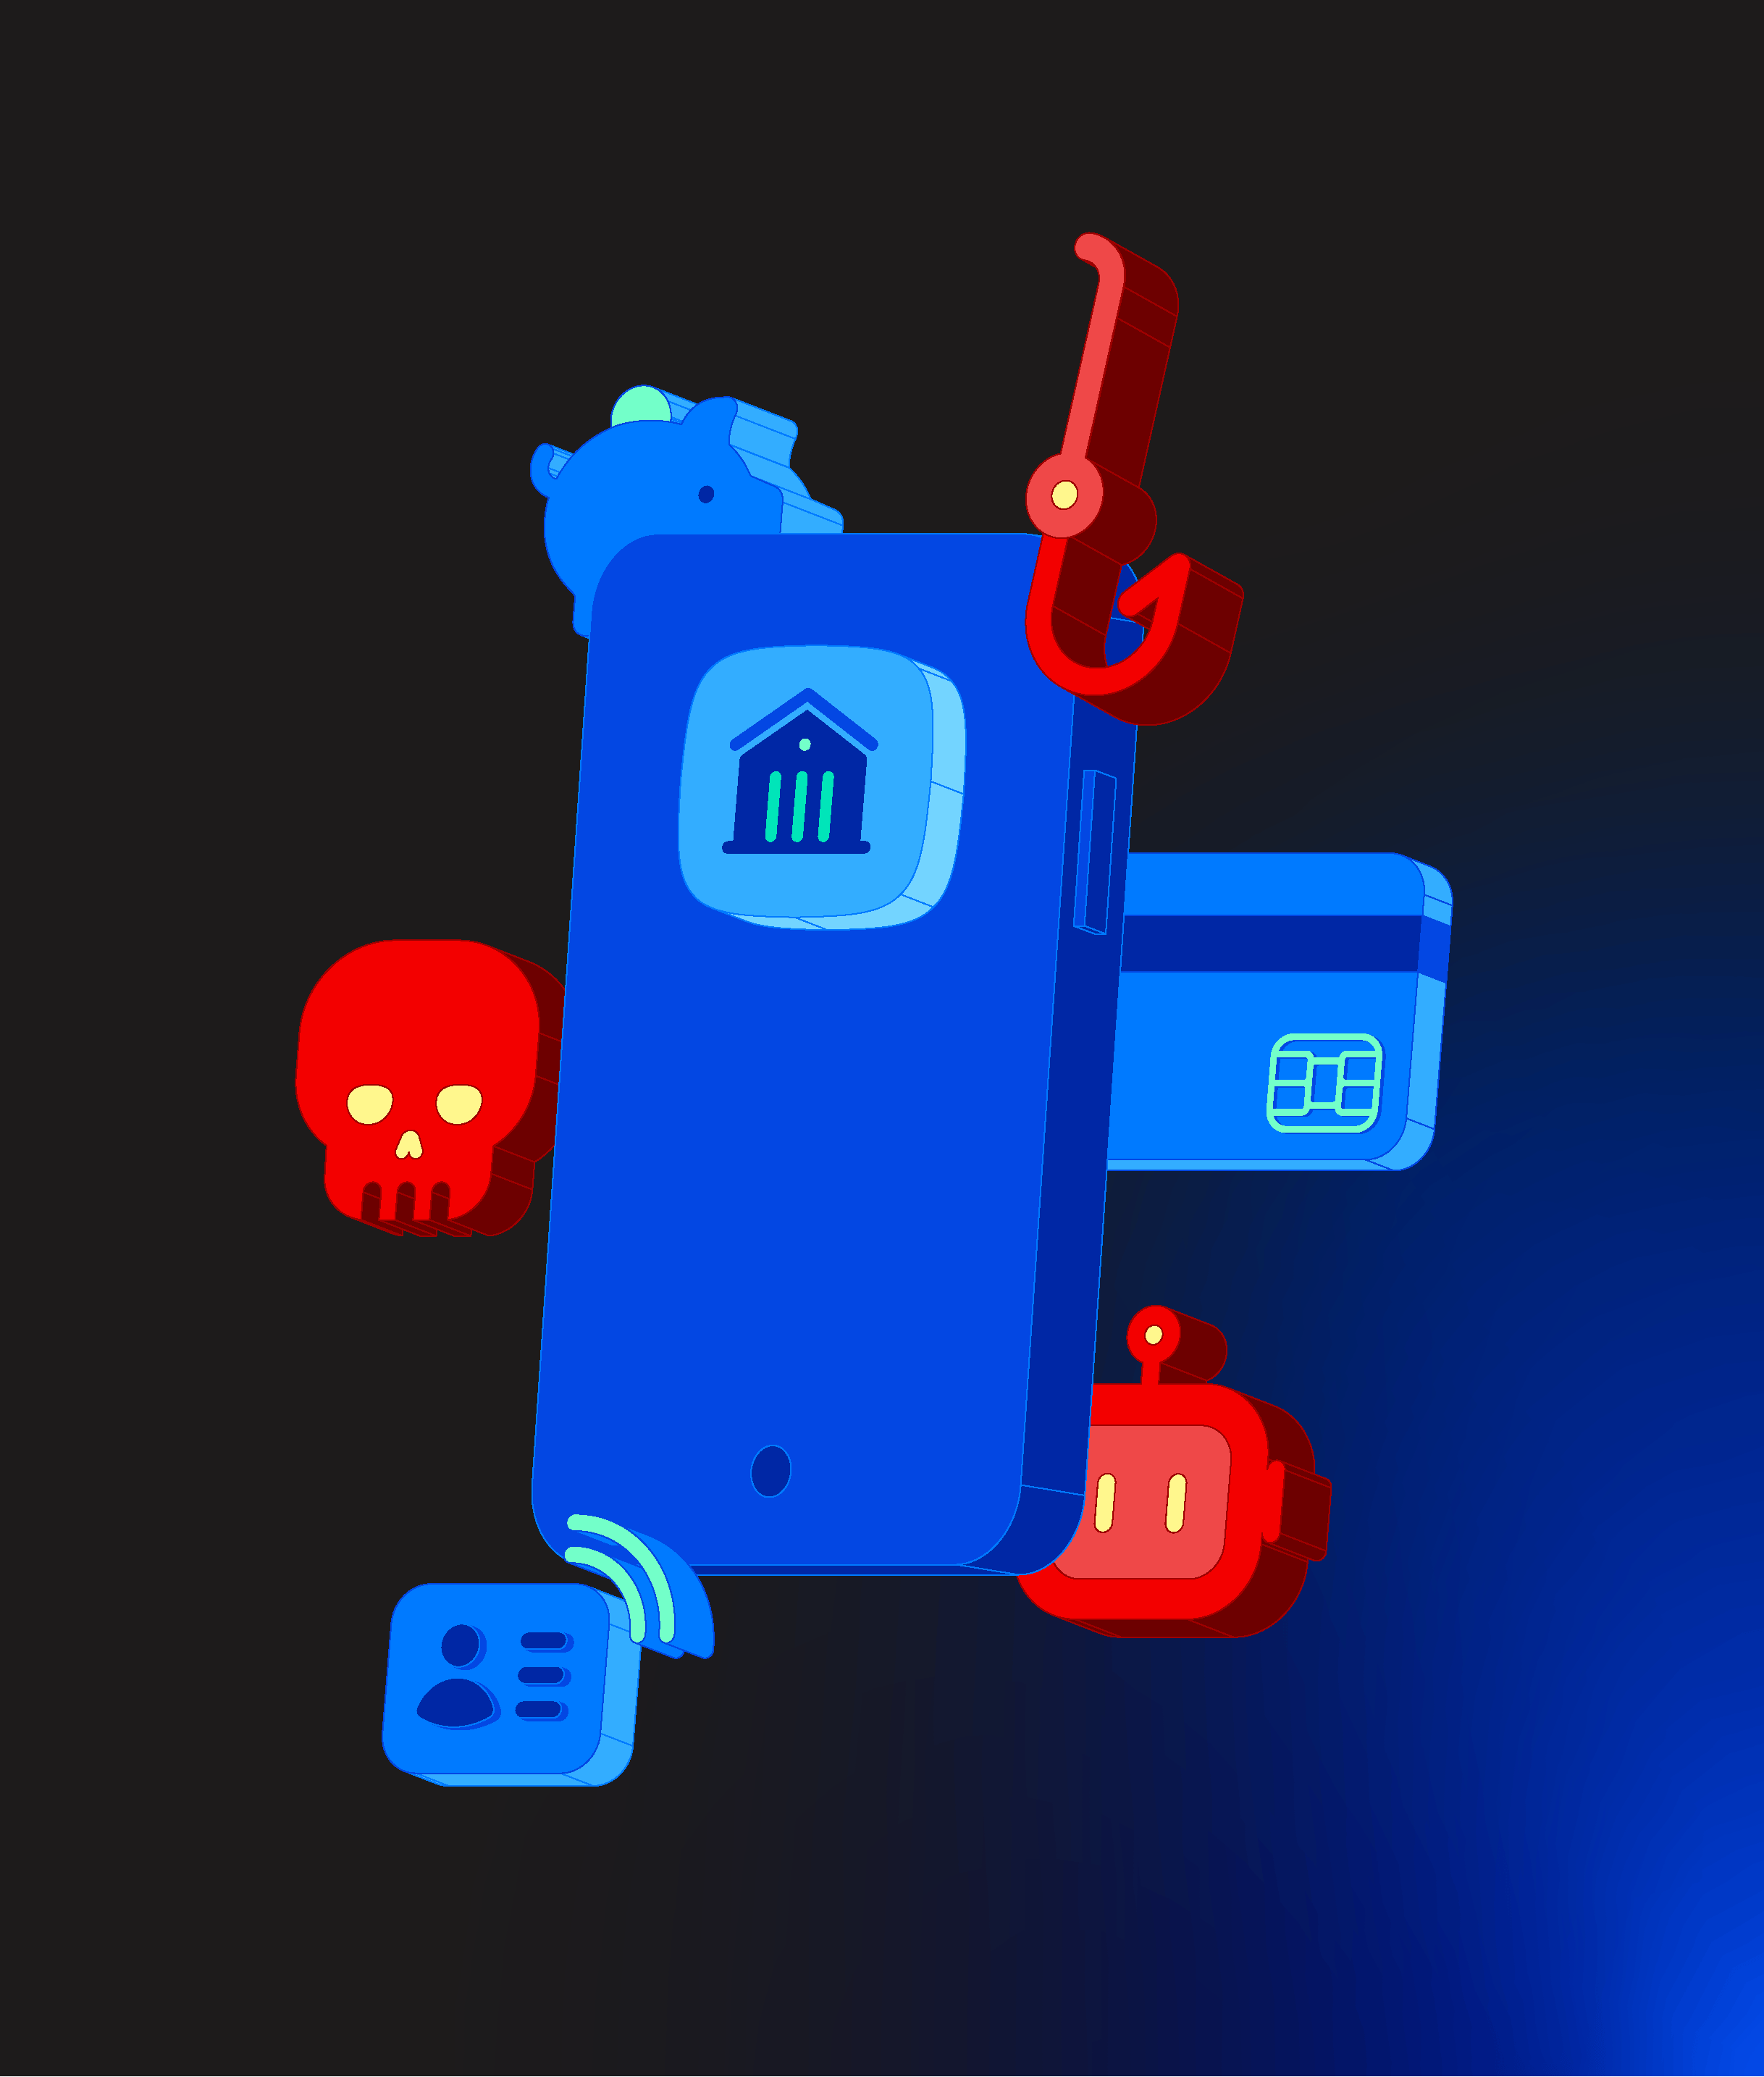
Mobile banking apps on unmanaged devices are constantly targeted by advanced malware and account takeover fraud. Common mobile banking app threats include:

  • Targeted malware that use overlays or abuse accessibility services to steal sensitive information.
  • Dynamic attacks that leverage hooking or injection to alter code behavior at runtime.
  • Reverse engineering and tampering that yields malicious cloned apps.
  • Mobile API abuse by automated bots, agents, or emulators.
01-BANKING-L_GRID-FRAUD_MALWARE_BOTS
02-BANKING-R_GRID-FULL-LIFECYCLE_MOBILE-APP-PROTECTION

Multi-layered protection across the mobile app lifecycle

Prevent fraud without compromising app performance or UX

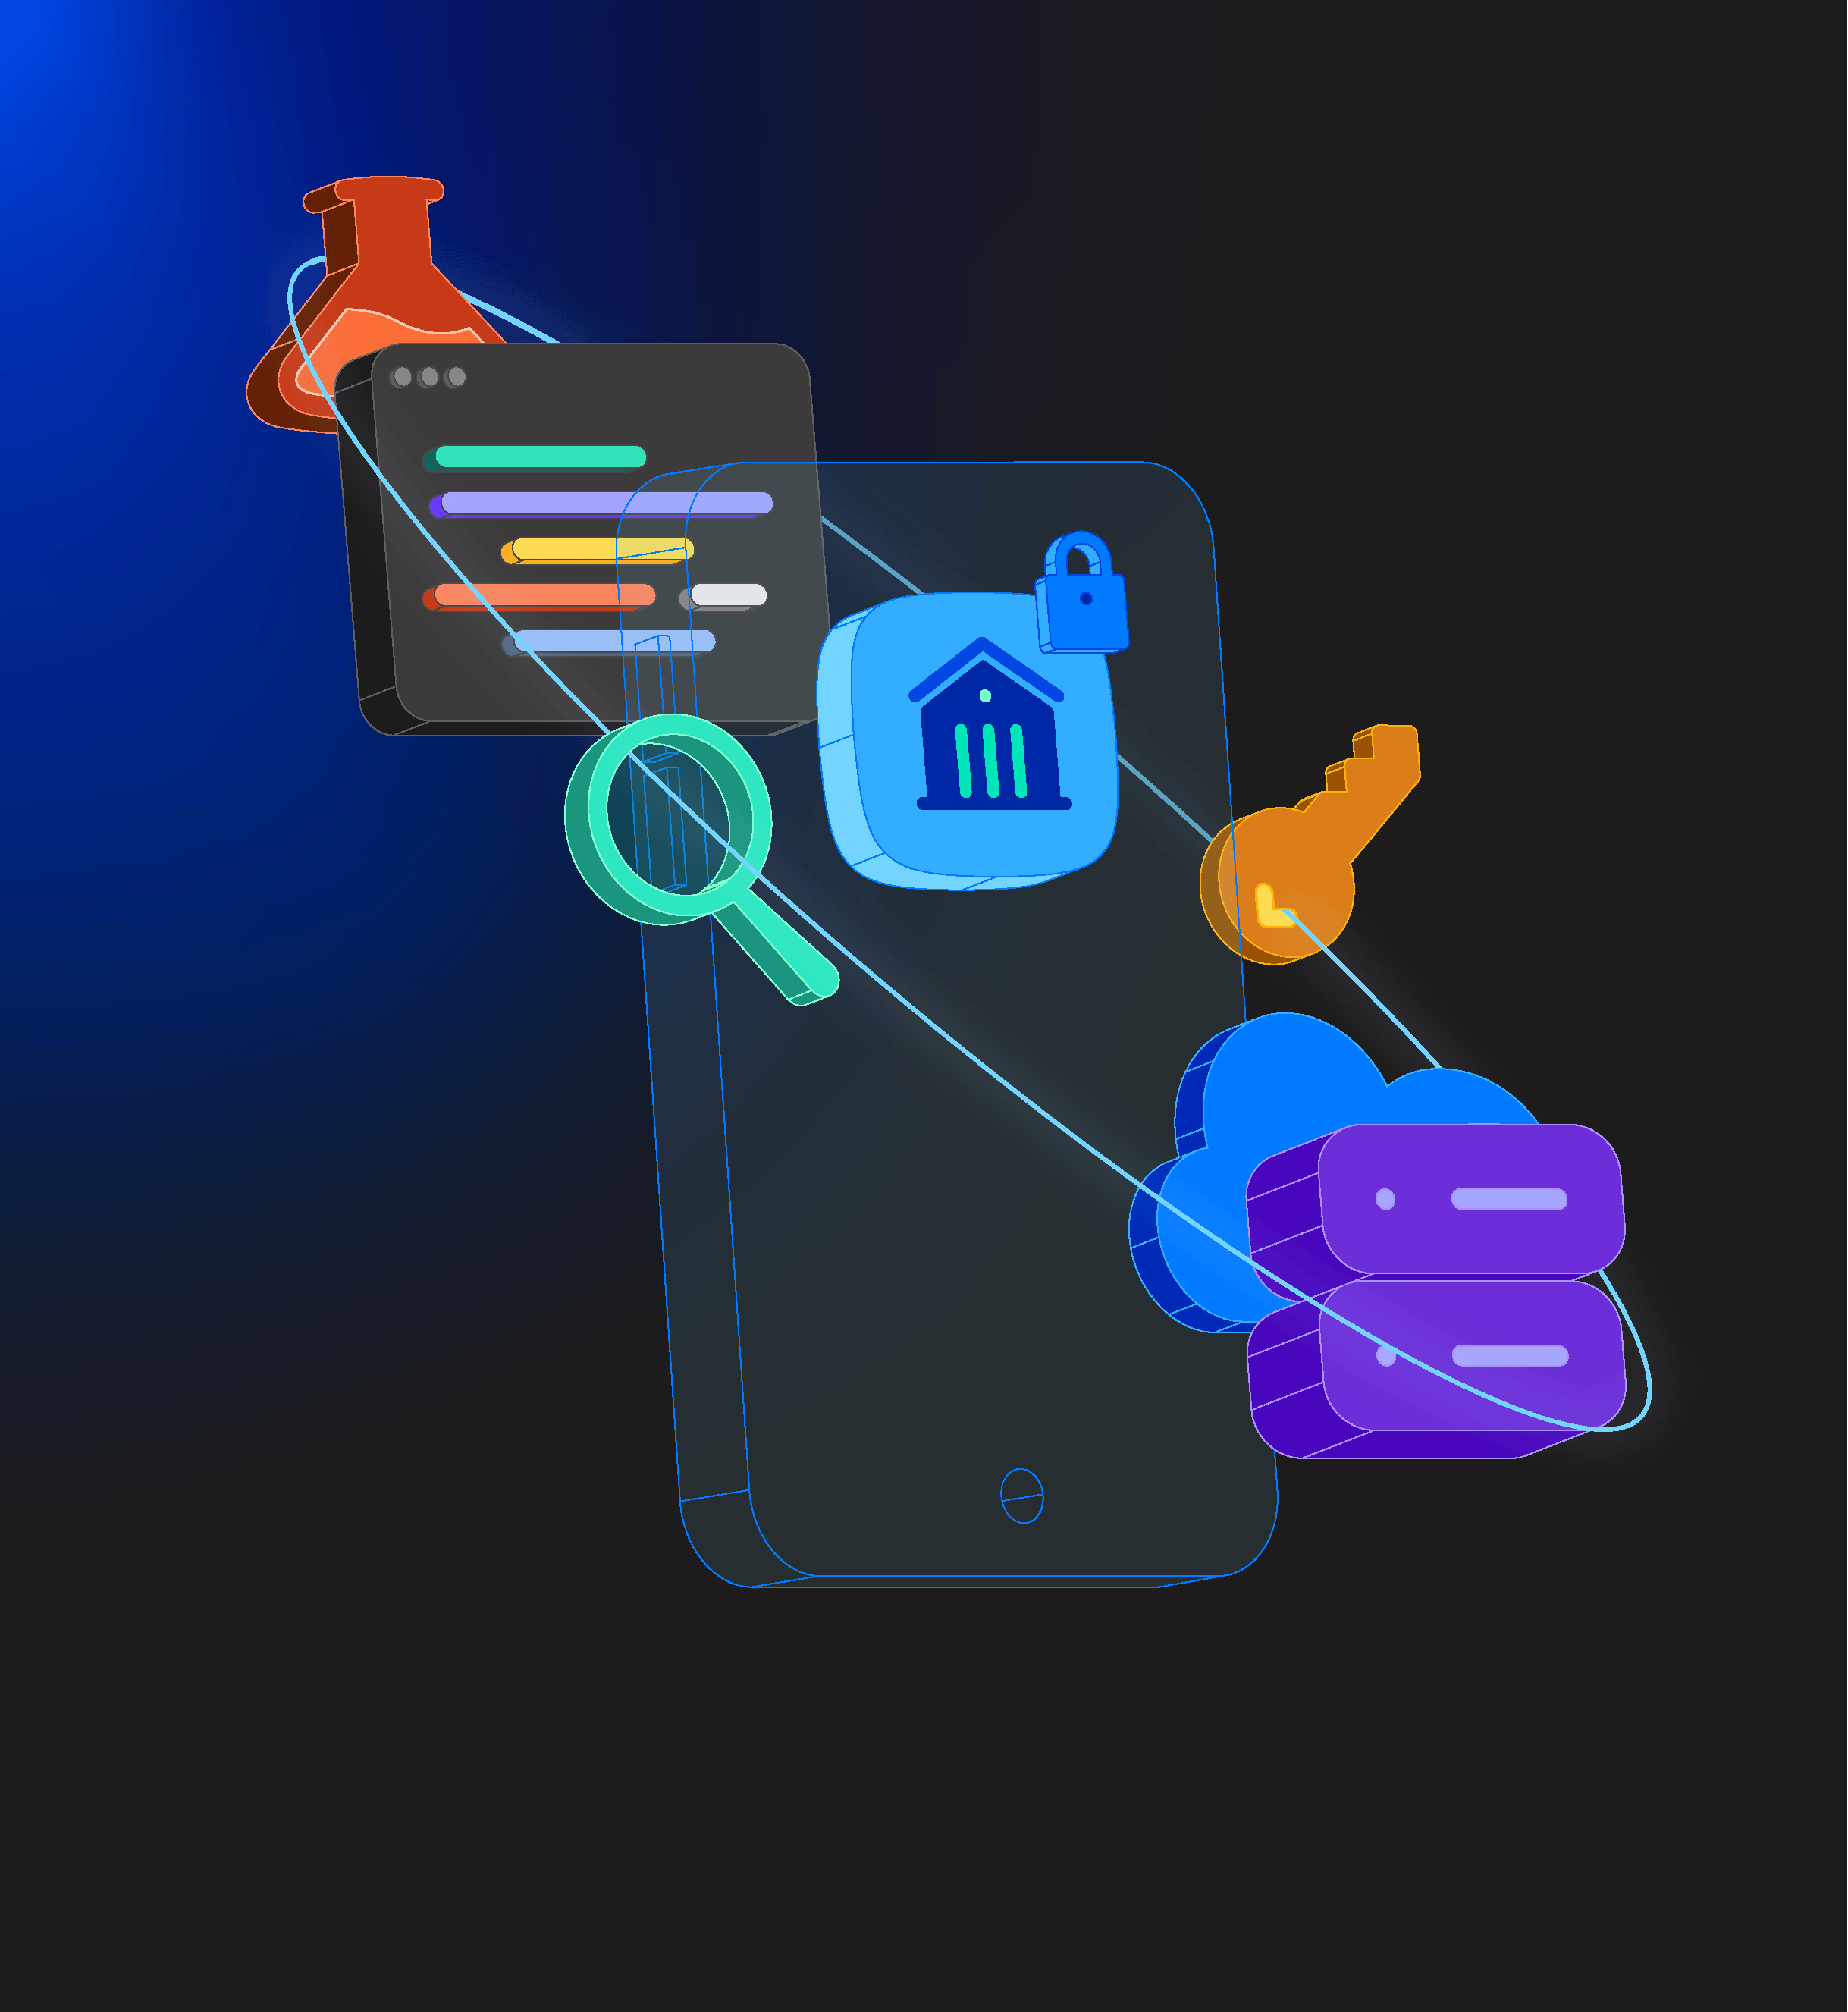
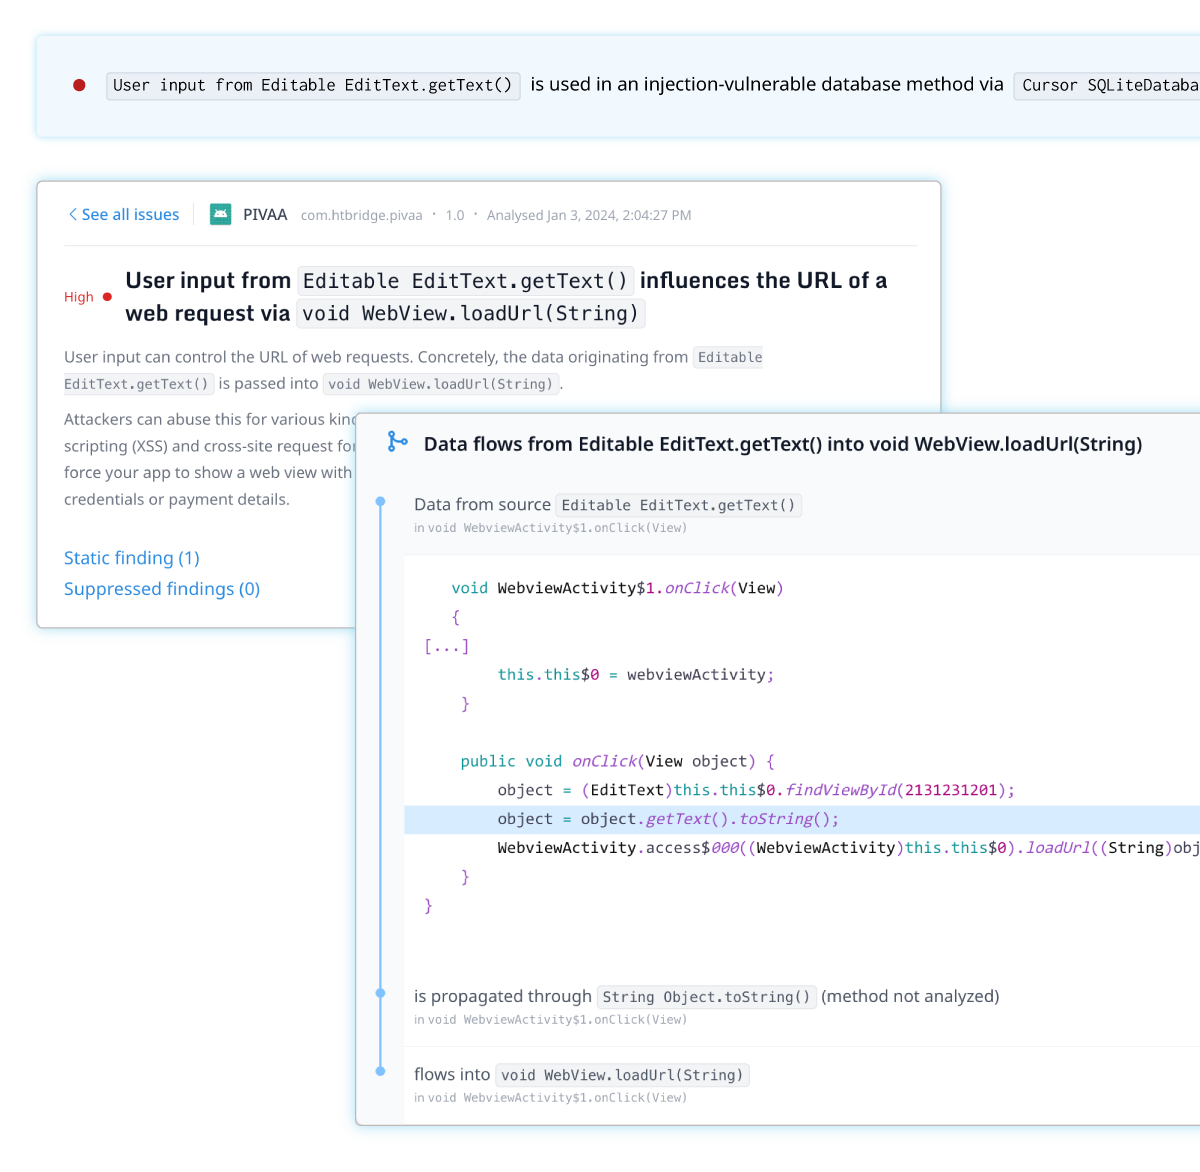
  • Modern mobile app security starts with continuous testing (MAST) to find and fix coding issues without disrupting development and delivery.
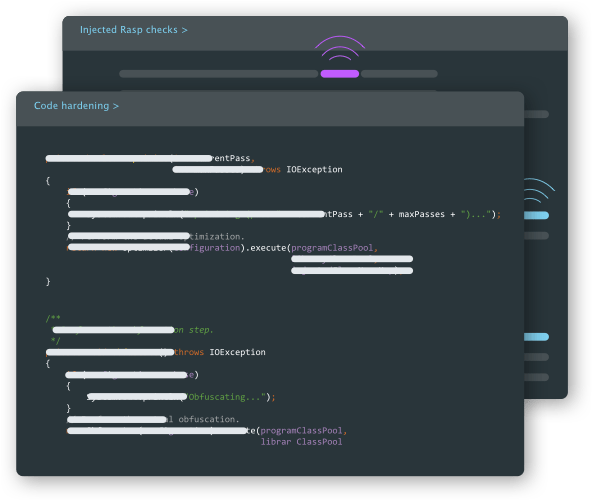
  • Multi-layered protections combine code hardening (obfuscation and encryption) and runtime checks (RASP) to detect threats like dynamic tampering and jailbroken or rooted devices
  • Dedicated API security (app attestation) ensures only genuine apps can access backend services, and real-time threat monitoring detects suspicious users and devices.
BOOST KYC WITH API SECURITY

API runtime defense against malware and fraud

Authenticate the integrity of your app before initiating financial transactions like P2P payments and fund transfers

  • Encrypt key documents and sensitive assets like PII, payment details, ID, API keys, etc.
  • Guarantee it’s your app attempting to interact with your APIs before granting access with cryptographic app attestation tokenization.
  • Reinforce protective measures to KYC implementation with the flexibility of dynamic, server-side configuration policies.
03-BANKING-L_GRID-API-RUNTIME-DEFENSE
Root Detetection_icon_04
Malware Protections

Prevent credential theft and deepfake authentication bypass with a polymorphic, defense-in-depth mobile app security strategy.

StandardPresentation_TESTING 3
Achieve Compliance

Satisfy both internal and external compliance regulations and requirements by protecting sensitive customer data.

StandardPresentation_MONITORING 1
Prevent Fraud

Improve existing MFA defenses with runtime protections, static code hardening, MAST, real-time threat monitoring and app attestation policies.

Safeguard your mobile banking ecosystem today

Secure banking built on trust

Simplify Compliance Requirements

Guardsquare’s complete security platform helps organizations address regulatory risks and compliance reporting requirements across all stages of the mobile app lifecycle.

AppSweep ANDROID & iOS

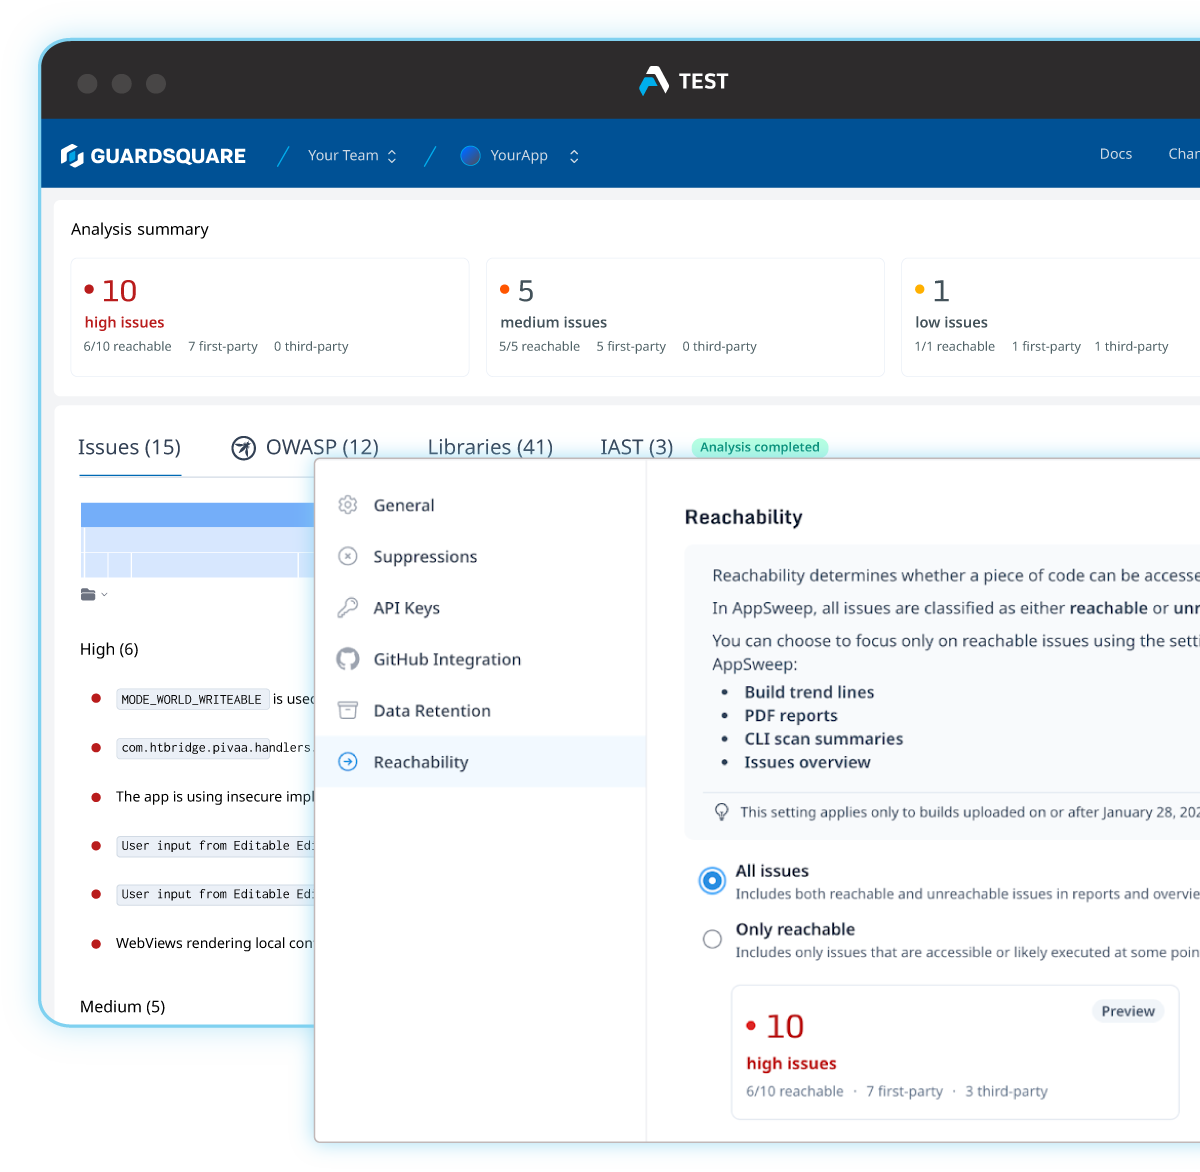
Find & address security issues in mobile apps and SDKs with AppSweep, our app security testing product. Designed for developers, ready for enterprise needs.

ThreatCast THREAT MONITORING

Monitor threats to mobile apps & SDKs in real time, adapt security configurations & identify security gaps & vulnerabilities post-publication.

Most mobile financial apps fall short of security best practices

We researched more than 3,000 of the world’s leading financial services apps on the Android marketplace and assessed their application shielding practices. Despite how essential mobile banking security is to the financial industry and its customer base:

< 0%
of financial apps apply best practices in mobile application security.

0%
of consumers who don’t use mobile payments cite security concerns as their main concern.

0%
of consumers are “very cautious” when sharing their financial data.

RASP in mobile banking refers to tools actively used to detect rooted or jailbroken operating systems, hooked environments (such as Frida or Xposed), emulator execution, and active debugging attempts, triggering automatic defensive actions or alerting security teams. With Guardsquare, this is accomplished via DexGuard (Android), iXGuard (iOS), and ThreatCast.

Guardsquare’ provides multi-layered defenses, including compiler-level code hardening, dynamic threat monitoring, and accessibility services protection. By obfuscating app logic and monitoring runtime environments, Guardsquare prevents banking malware from abusing Android accessibility services, capturing keystrokes, injecting fraudulent overlay screens, or intercepting OTP tokens.

Guardsquare fulfills critical regulatory mandates for mobile payments—including PCI MPoC (Mobile Payment on COTS), PSD2 Strong Customer Authentication (SCA), and PCI DSS—by enforcing binary code protection, cryptographic key protection, and runtime integrity attestation. This ensures tap-to-phone (SoftPOS) and digital wallet applications process transactions securely on unmanaged mobile devices.

Yes. Standard compliance frameworks like OWASP Mobile Application Security Verification Standard (MASVS) explicitly mandate code hardening and anti-tampering measures (MASVS-RESILIENCE) for financial apps.

Guardsquare applies advanced, polymorphic obfuscation (control flow flattening, arithmetic obfuscation, string encryption) to exceed MASVS requirements and prevent reverse engineering.

No. Unlike legacy binary wrappers that add execution overhead, Guardsquare’s DexGuard (Android) and iXGuard (iOS) operate directly inside the build pipeline at the compiler level.