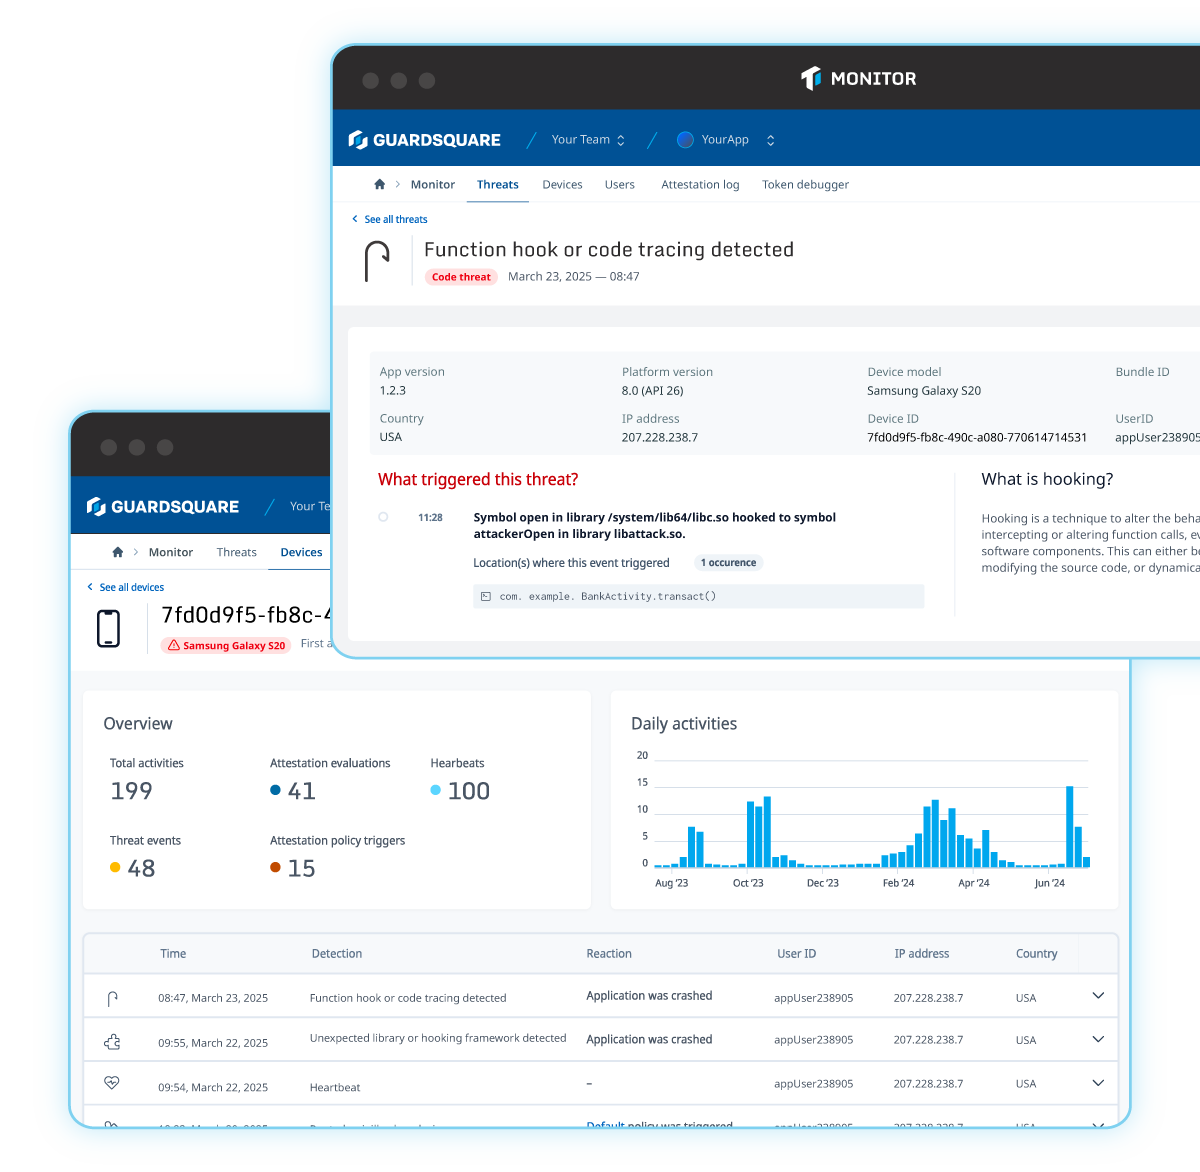
Regulatory compliance with built-in audit evidence

Comply confidently

MOBILE APP COMPLIANCE

Regulations set minimum standards for security

Regulatory standards for mobile apps (like banking, medical devices, and embedded payments) establish a baseline for protecting sensitive user data.
  • Translate broad mandates into specific technical controls.
  • Meet the requirements of PCI, PSD2, PSD3, and regional data privacy laws without grinding your release cycles to a halt.
01_REGULATORY-COMPLIANCE-L_GRID-REGULATIONS-02
02_REGULATORY-COMPLIANCE-R_GRID-EVIDENCE-01
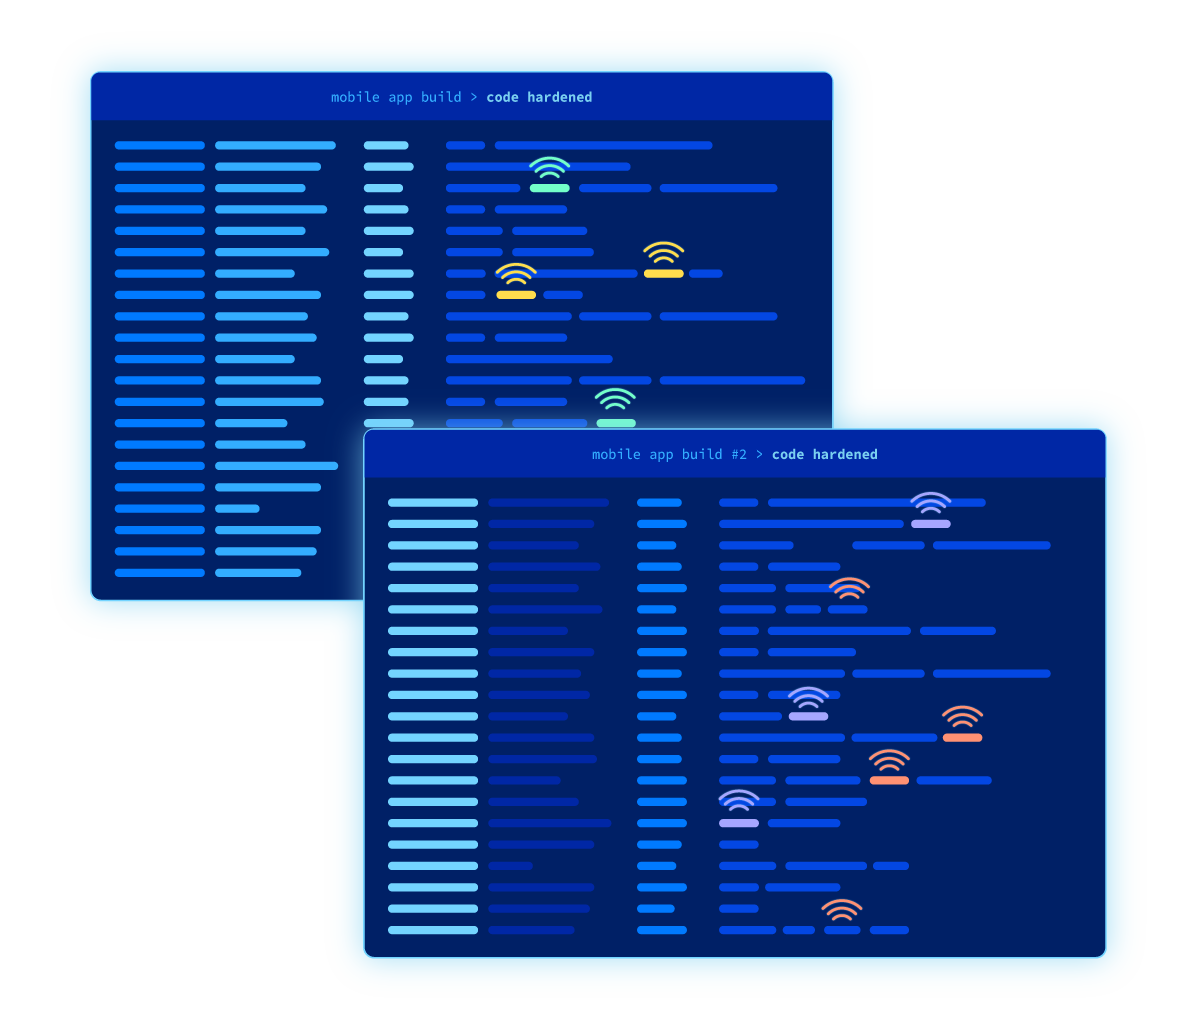
AUDIT-READY TELEMETRY

Generate clear audit evidence for PCI MPoC, PCI DSS, PSD2, and PSD3 mandates

Regulated industries require end-to-end evidence from pre-release security testing reports to live runtime threat logs.

  • Automated alignment with OWASP MASVS benchmarks.
  • Live runtime threat telemetry categorized by environment, app, and code threats.
  • Zero-friction integration into existing build automation tools.
HEALTHCARE COMPLIANCE

Secure Mobile Health (mHealth) and SaMD to Fulfill FDA and EU-MDR Requirements

Streamline FDA, EU-MDR, and ISO compliance by integrating automated mobile security testing, multilayered code protection, and real-time threat monitoring into the SDLC.
  • Mitigate application tampering and sabotage risks under EU-MDR Section D.3.2.3.
  • Align with IEC 62304 and ISO 14971 risk management software standards.
  • Prevent costly data breaches and regulatory fines by embedding security into CI/CD.
03_REGULATORY-COMPLIANCE-L_GRID-MHEALTH-01
SECURITY-TESTING-ICON-300
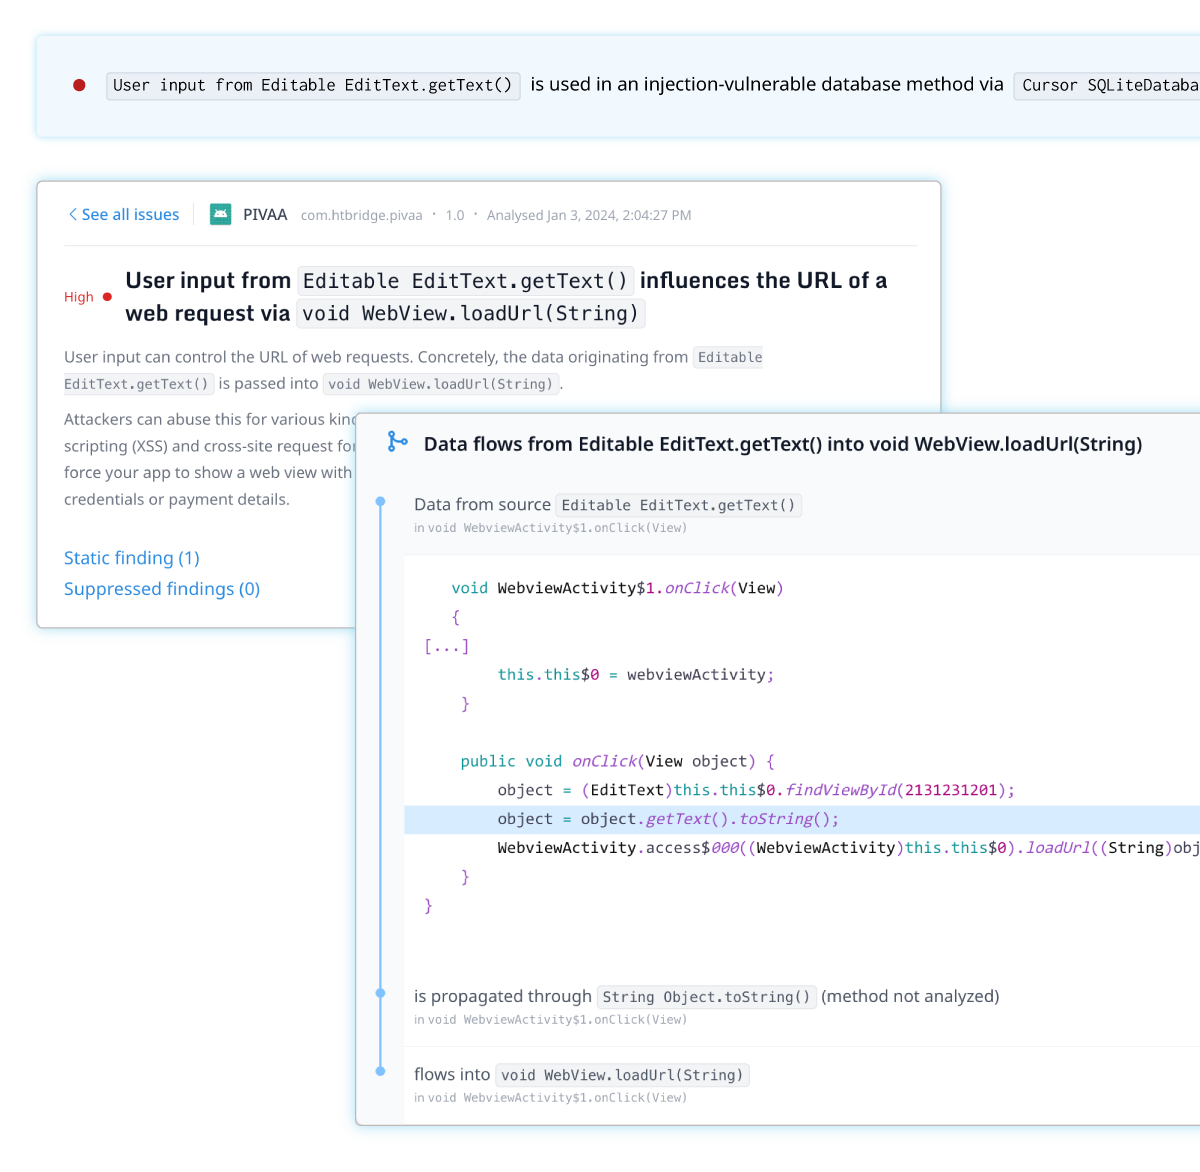
Automated security testing

Identify security gaps early with automated testing integrated into CI/CD pipelines.
OBFUSCATION-ICON-300
Multilayer protection

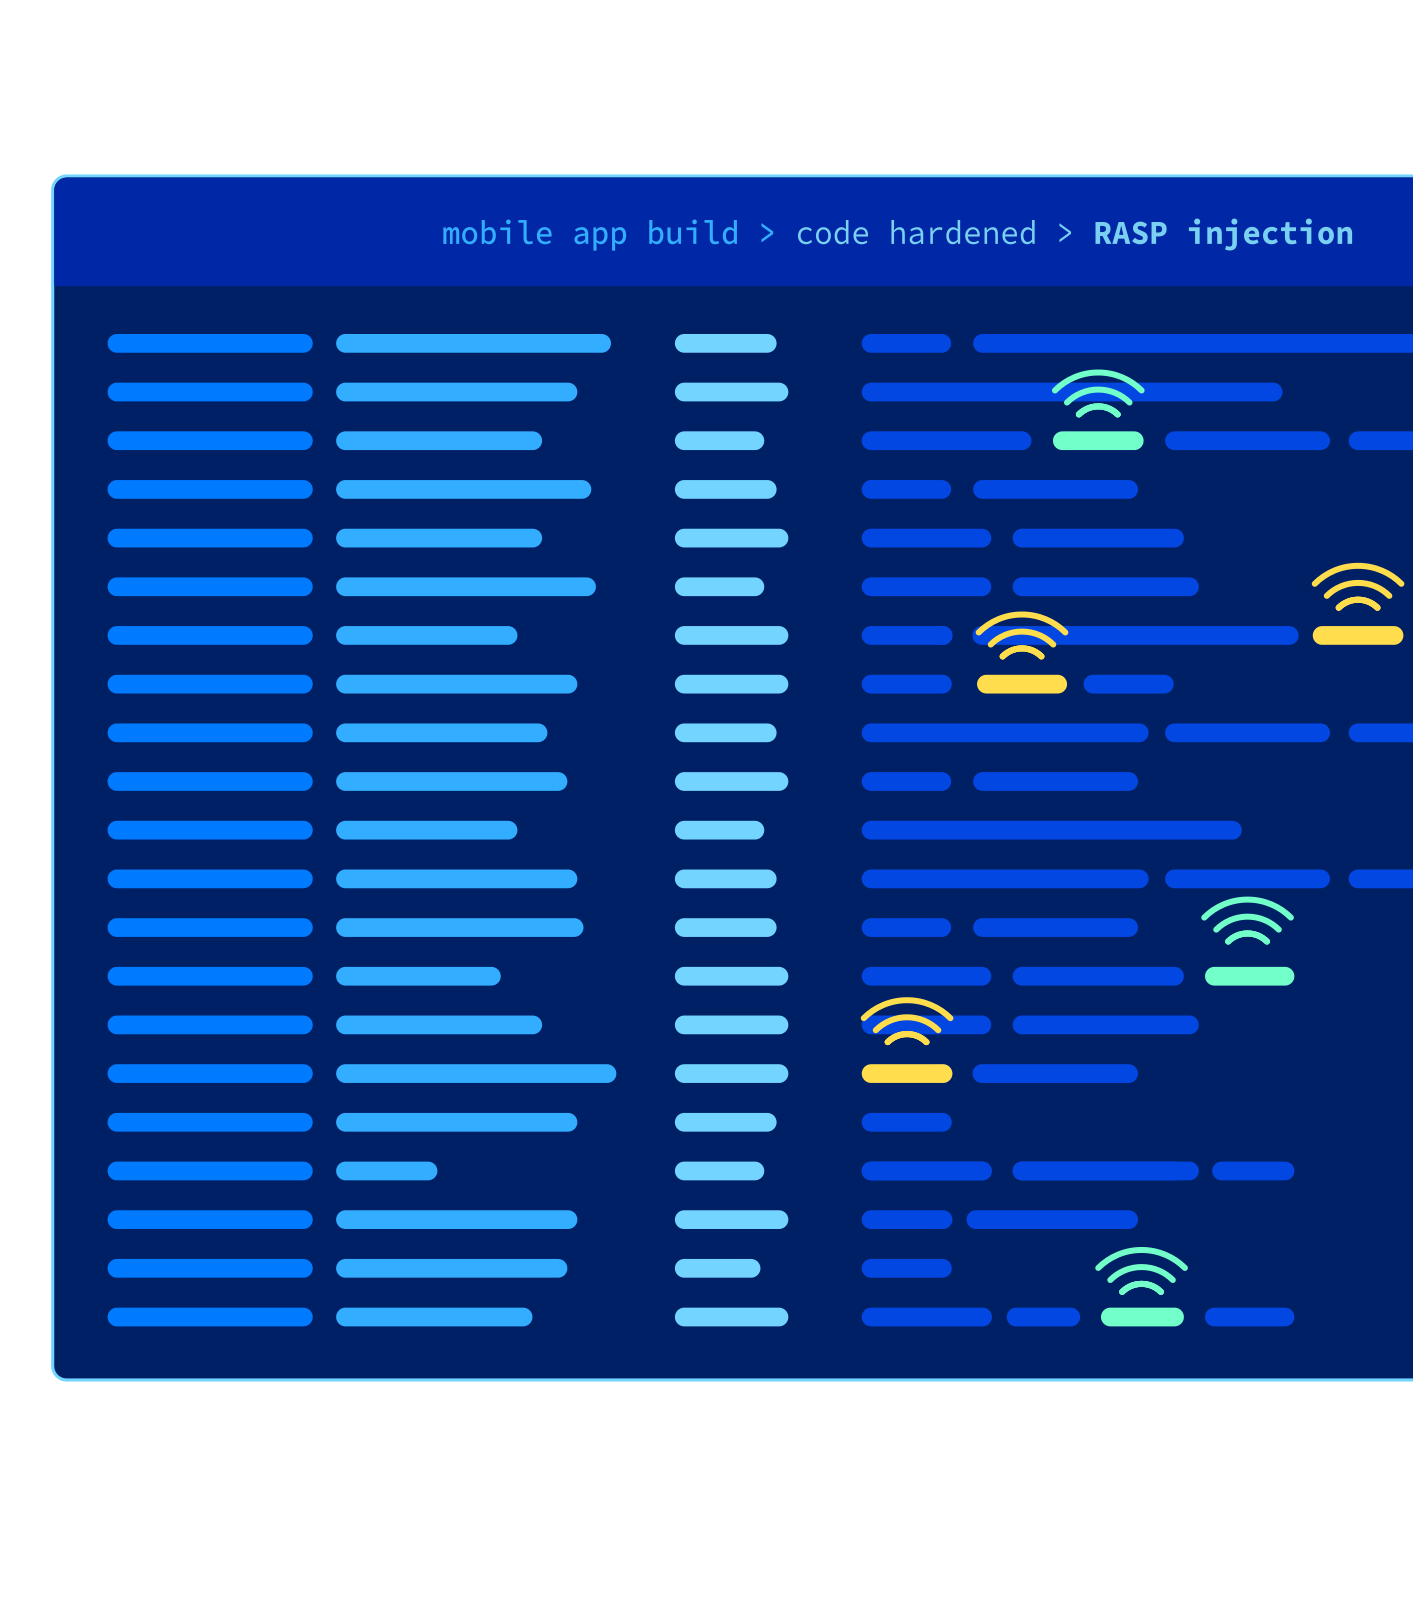
Prevent reverse engineering with code hardening and dynamic RASP checks.
PREVENT-FRAUD-ICON-300
Real-time monitoring

Gain continuous visibility into runtime threats.

Stop scrambling for audit evidence. Build compliance directly into your CI/CD pipeline today.

Why every organization should prioritize compliance

Compliance should be part of mobile app development instead of a mandatory afterthought

0%
of security leaders struggle with getting developer buy-in.

0%
of developers state compliance as a top investment driver for a security solution.

0%
of popular mHealth apps fail to meet at least one of the seven OWASP MASVS categories.

Build compliance into the SDLC

Simplify Compliance Requirements

Guardsquare’s complete security platform helps organizations address regulatory risks and compliance reporting requirements across all stages of the mobile app lifecycle.
AppSweep ANDROID & iOS

Find & address security issues in mobile apps and SDKs with AppSweep, our app security testing product. Designed for developers, ready for enterprise needs.
ThreatCast THREAT MONITORING

Monitor threats to mobile apps & SDKs in real time, adapt security configurations & identify security gaps & vulnerabilities post-publication.

Guardsquare provides multi-layered code obfuscation, resource encryption, and RASP checks to safeguard cardholder data and cryptographic keys in mobile payment and SoftPOS apps.

Yes, Guardsquare protects Strong Customer Authentication (SCA) implementations and secure communication interfaces against reverse engineering and tampering, satisfying key PSD2 RTS clauses.

No. DexGuard and iXGuard operate as command-line, post-build compiler tools locally or on your CI/CD server, preserving complete source code privacy.

ThreatCast delivers real-time threat logging and monitoring, providing documented evidence of runtime protection and active threat defense.

Compiler-based protections are optimized for performance and will have minimal impact on app performance.

Yes, DexGuard protects Android apps while iXGuard protects iOS apps, both managed seamlessly under ThreatCast monitoring.