FinTech mobile app security

FinTech

FRAUD AND REGULATORY RISKS

Financial apps face rising attacks and compliance repercussions

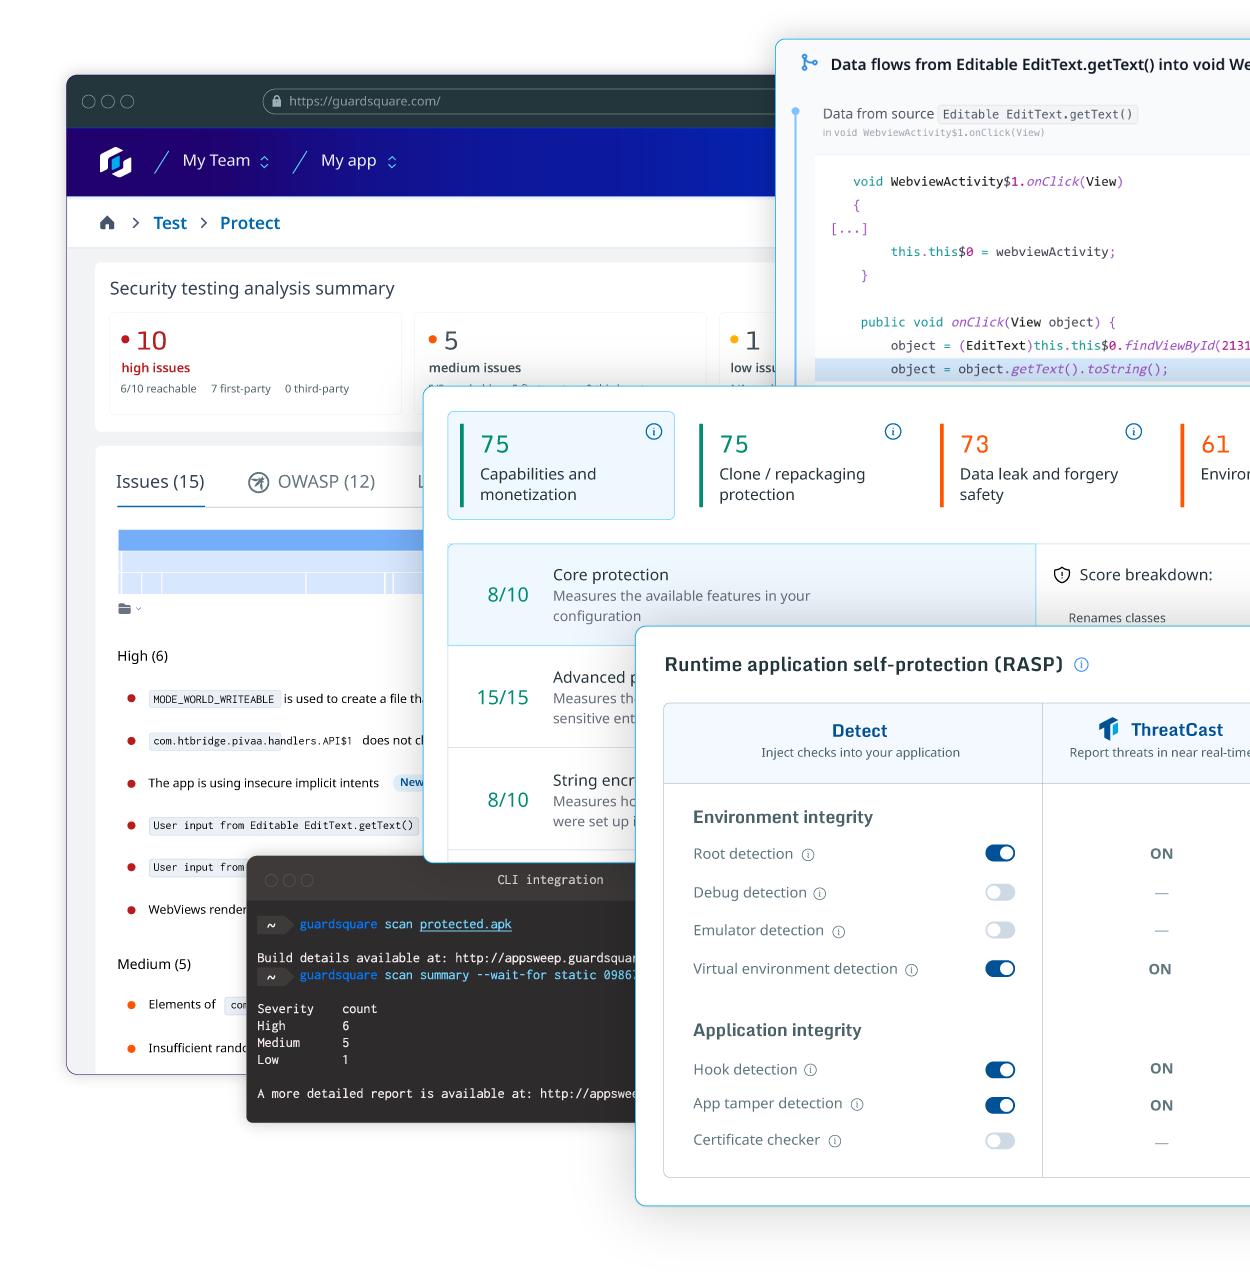
Successful mobile fraud attacks can extract hard-coded secrets, bypass KYC controls and trigger regulatory fines and negative publicity.
  • Protect against credential theft and unauthorized account access
  • Stop malicious actors from bypassing KYC and authentication controls
  • Prevent API abuse from bots, scripts, and repackaged clones
01-FINTECH-L_GRID-FRAUD_REGULATORY_RISKS_001
02-FINTECH-R_GRID-MULTILAYERED-FRAUD-PROTECTIONS_001
MOBILE SECURITY AND COMPLIANCE

FinTech apps need multilayered fraud protections

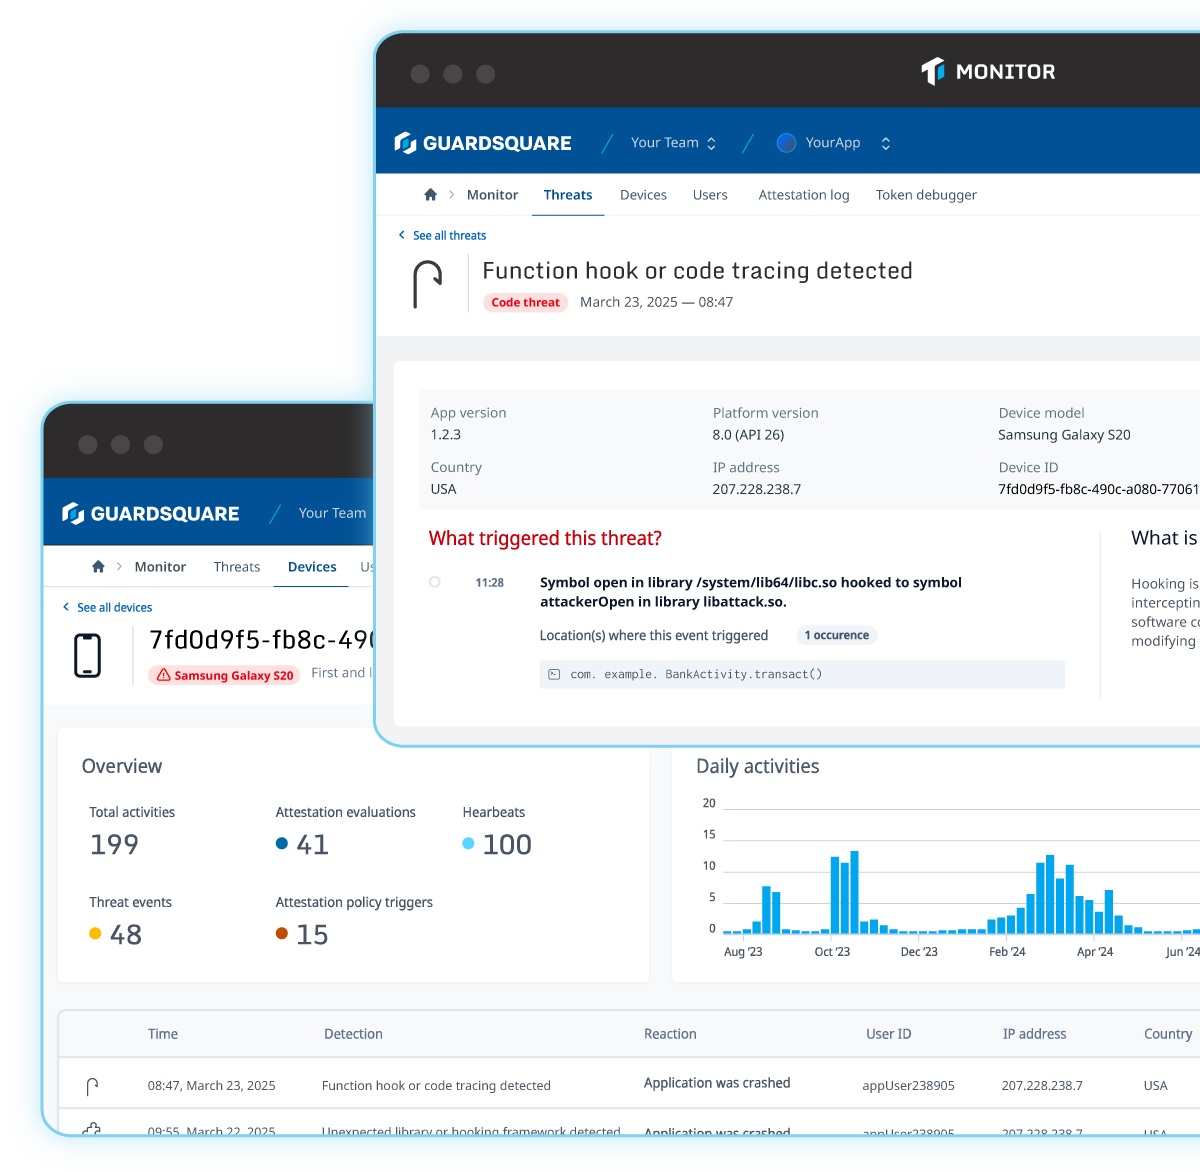
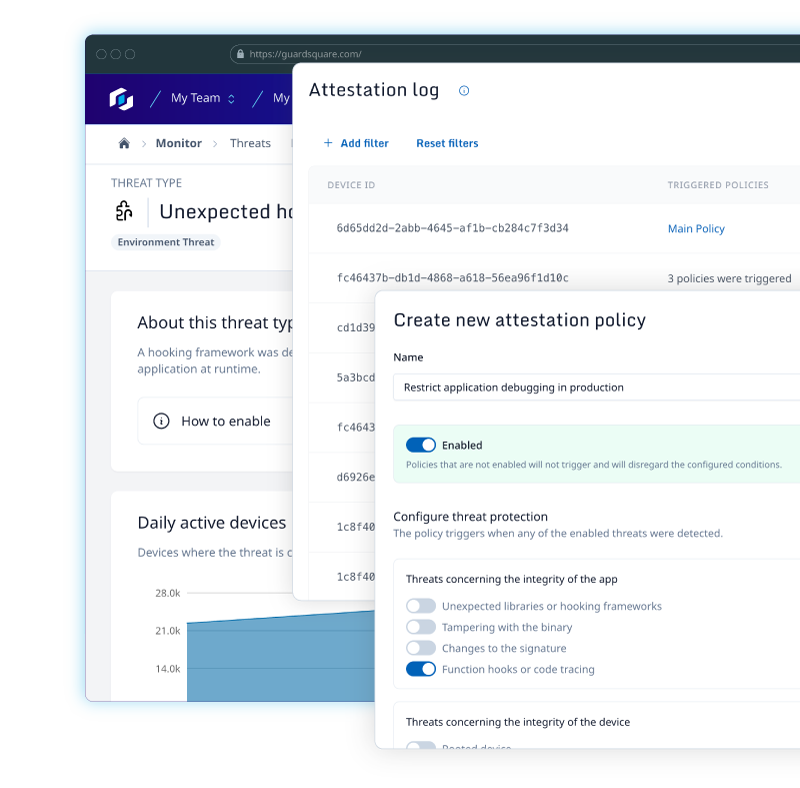
Scan your code for vulnerabilities, implement strong protections including advanced code hardening and RASP checks, and apply dedicated mobile API security to protect your backend servers.
  • Prevent mobile app cloning and tampering with in-depth code hardening and runtime security checks (RASP)
  • Ensure only legitimate devices are interacting with your APIs
  • Maintain compliance with mandates and regulatory requirements like PCI MPoC,PSD2 and PSD3
Achieve_Compliance-icon-300
Meet Compliance

Meet regulations and compliance mandates by protecting sensitive customer data.
MULTILAYERED-PROTECTIONS-ICON-02-300
Protect Against Fraud

Prevent credential theft and deepfake bypass authentication with in-depth, multilayered code obfuscation and RASP checks.
GLOBE-ICON-300
Build Brand Trust

Improve adoption rates and customer retention by proving that FinTech mobile app security has been a priority throughout the entire SDLC.

Start protecting your FinTech mobile apps with Guardsquare today

Secure financial apps and SDKs

Why FinTech mobile apps need advanced security

FinTech is among the most targeted industries for malicious actors

0%
of all data breaches directly target the FinTech industry.

0%
increase in mobile banking trojans detected in H1 2025 YoY.

0%
of all FinTech security incidents originate in third-party vendors SDKs.

Explore Fintech resources

Yes, Guardsquare’s in-depth, multi-layered protections can help FinTech organizations meet compliance and regulatory goals such as PSD2, PSD3, and PCI.

FinTech mobile apps are prime targets for fraud attacks, and can carry significant compliance risks. That is why a compiler-based approach with multiple layers of protection provides the best defense against ever-evolving threats.

Credential theft via malware, fake or cloned apps distributed through phishing campaigns, and runtime manipulation (e.g., hooking or injection) are some of the most common attacks against FinTech mobile apps. Guardsquare provides multi-layered protections against both static and dynamic analysis, largely mitigating these threat vectors.

Android and iOS both provide sandboxing and permission controls to protect the user and their device. But they do not protect your compiled application code from being reverse engineered, modified, or instrumented at runtime. That is why an in-depth, dedicated mobile application security strategy is essential.

Guardsquare's protections have negligible impact on app size and performance in most cases. FinTech clients generally report no measurable degradation in startup time or responsiveness of their mobile app.