Advanced malware protection and security

Stay ahead of attackers

MOBILE MALWARE

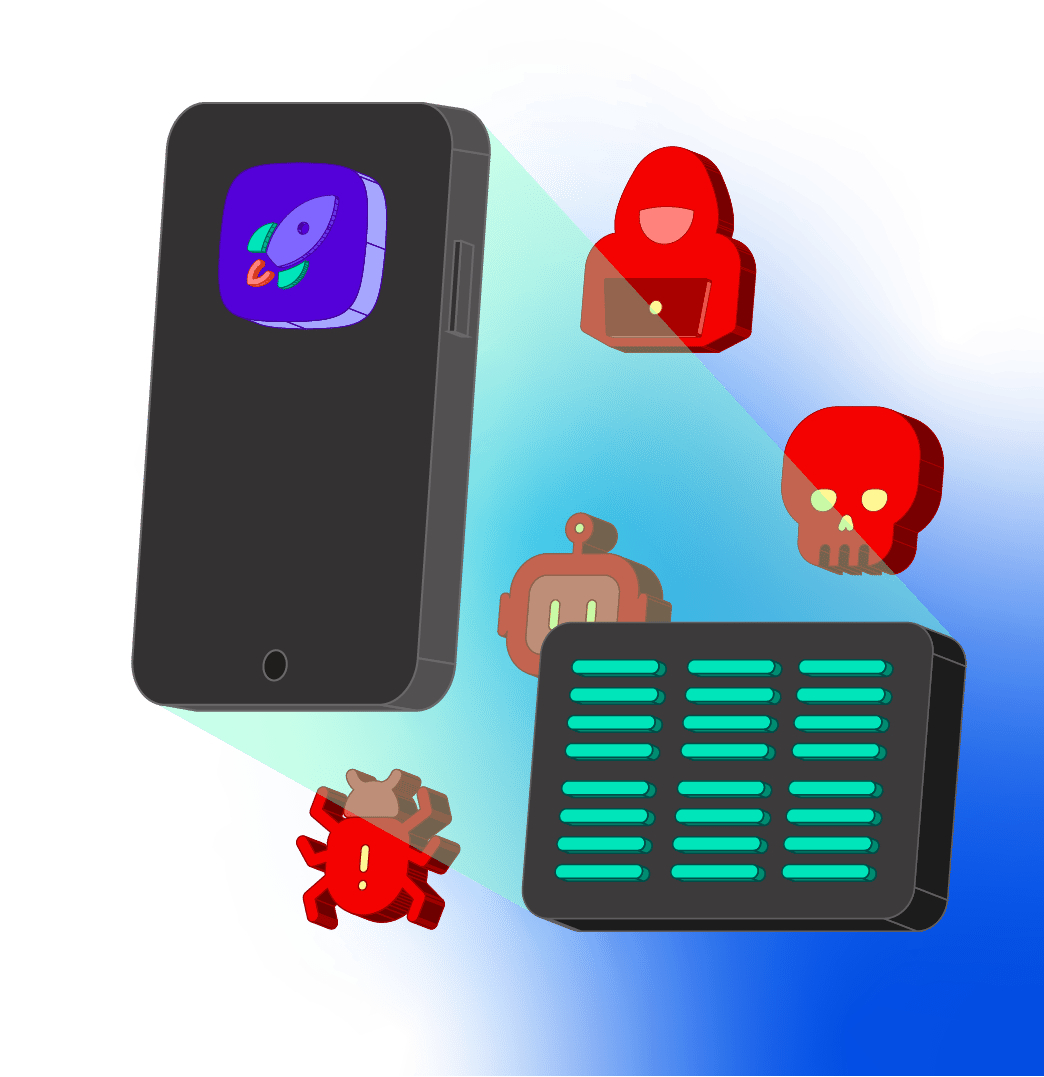
Evolving malware bypasses basic OS protections

Modern malware continuously evolves, finding new ways to exploit the Android OS to target sensitive applications on user devices.
Common strategies include:

  • Accessibility (a11y) services abuse for automated fraud.
  • Overlays/UI injections to steal credentials.
  • Screen recording and keylogging.
01_MALWARE-PROTECTION-L_GRID-EVOLVING-THREATS-01
02_MALWARE-PROTECTION-R_GRID-SECURE-01
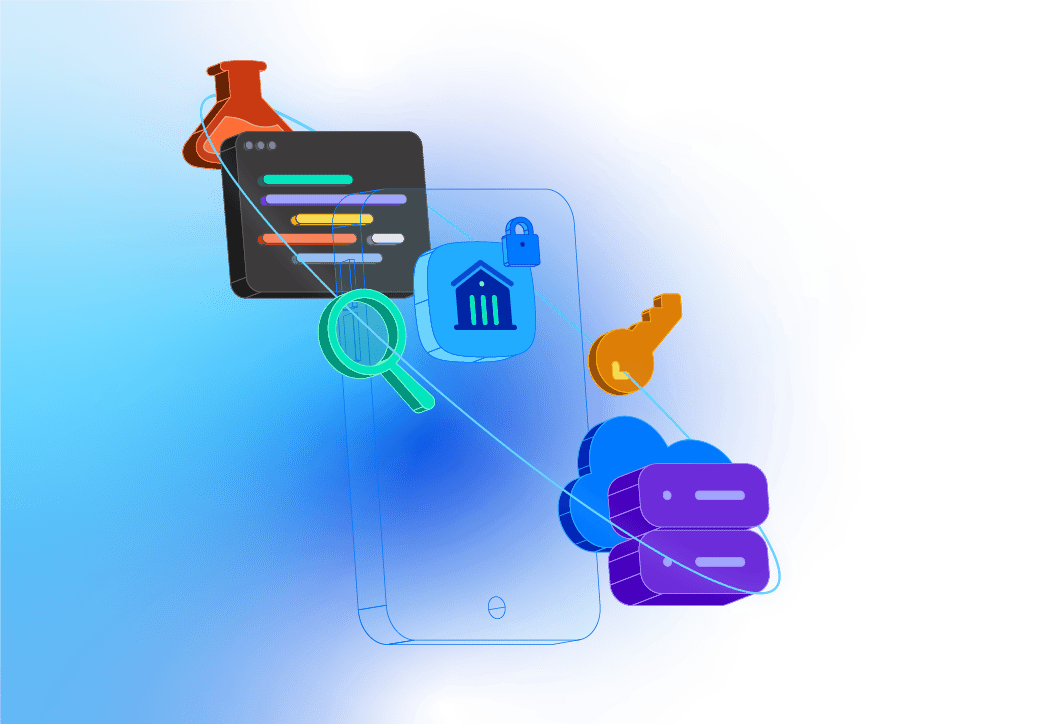
MULTI-LAYERED PROTECTION

Securing sensitive transactions from malware-assisted fraud

Mobile applications for banking, P2P payments, crypto, and digital wallets are high-value targets for malware. To stop these attacks, developers need a modern defense strategy that actively prevents malware from hooking into the application environment.

SECURITY-TESTING-ICON-300
Secure coding

Continuous, purpose-built mobile app testing based on OWASP MAS open standards.

OBFUSCATION-ICON-300
Multilayered protection

Multiple layers of static and dynamic protections that harden mobile code and actively prevent reverse engineering and tampering attacks.

PREVENT-FRAUD-ICON-300
Situational awareness

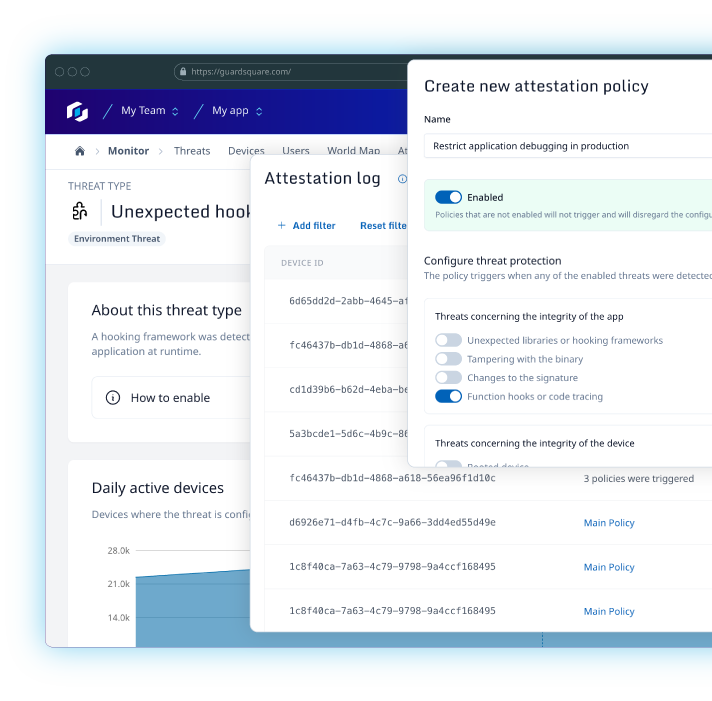
Real-time threat monitoring provides important forensics and insights while app attestation protects mobile APIs and backend services from abuse.

Stop malware-assisted fraud attacks before they start

Mitigating malware exposure

Protection against modern malware

The Guardsquare platform combines industry-leading security solutions for continuous testing, multi-layered protections, real-time threat monitoring, and dedicated mobile API security.

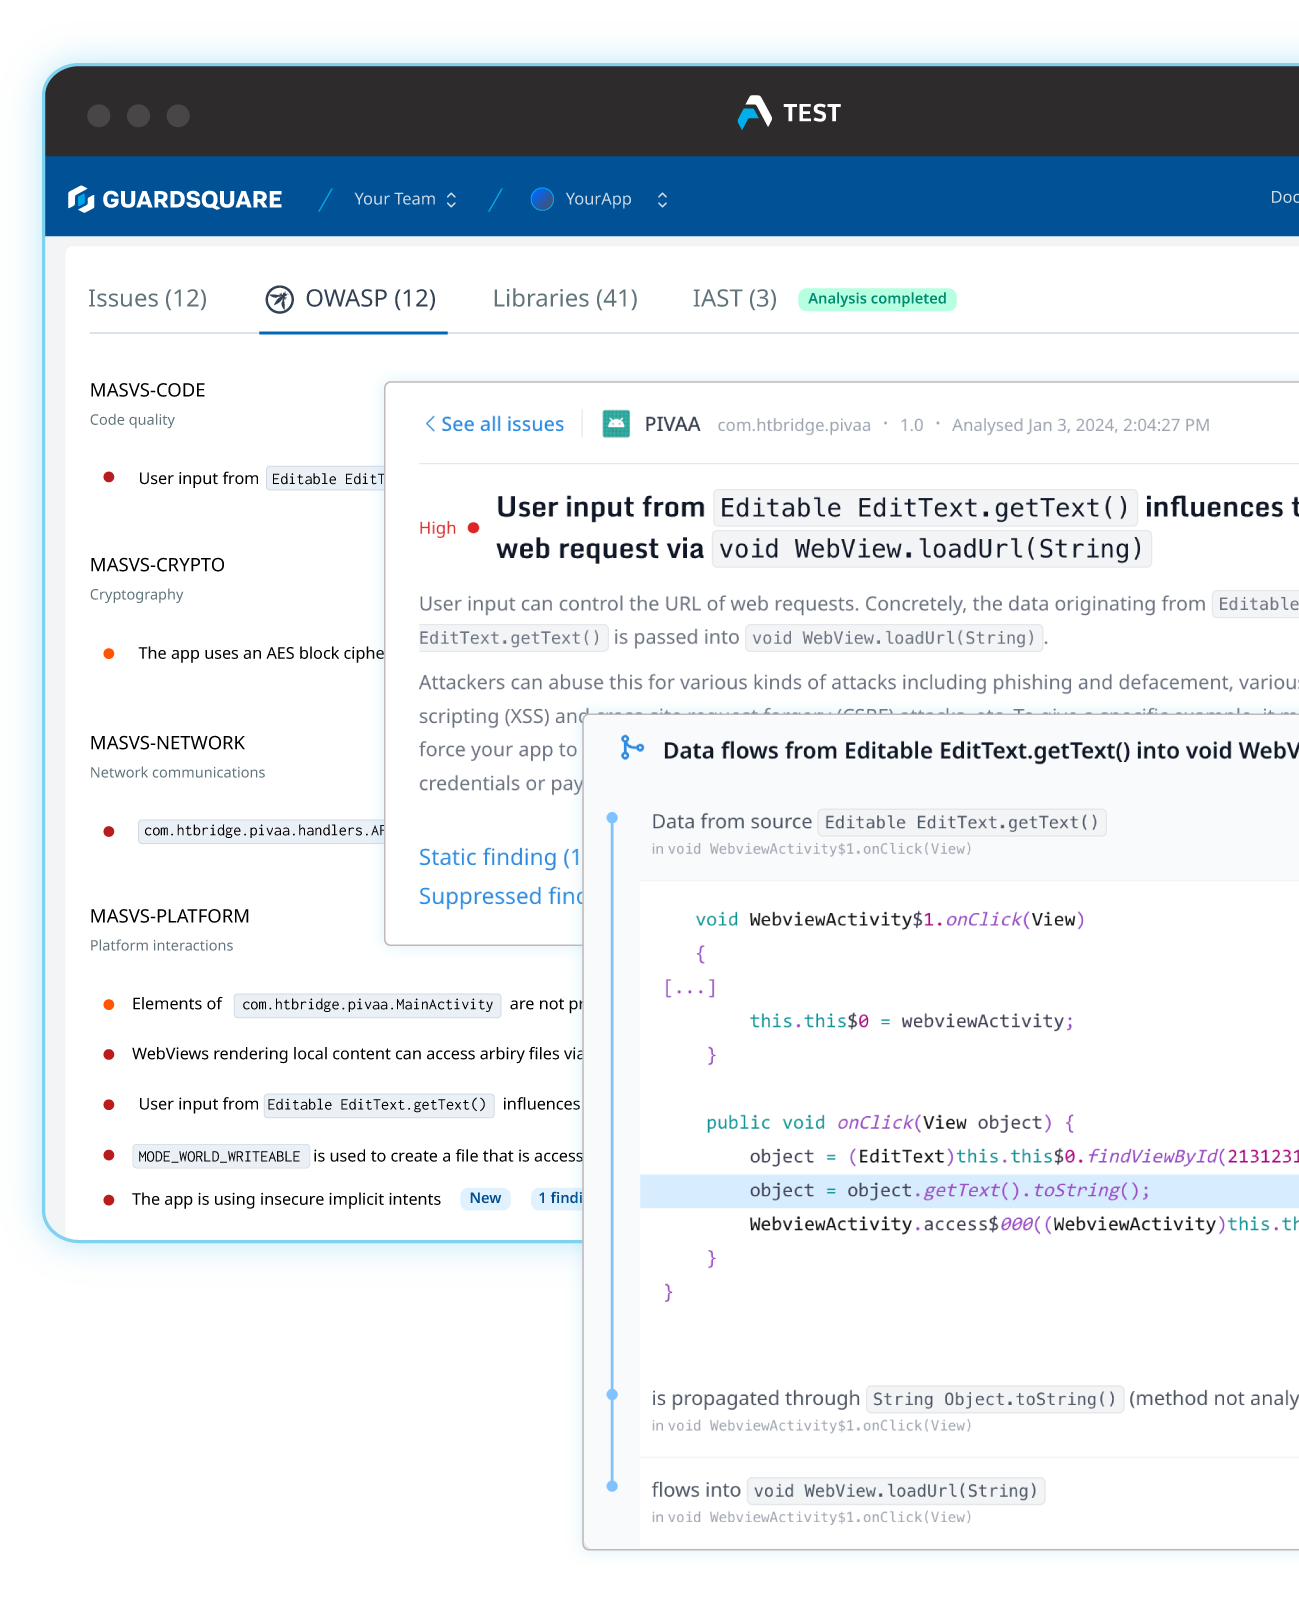
AppSweep ANDROID & iOS

Find & address security issues in mobile apps and SDKs with AppSweep, our app security testing product. Designed for developers, ready for enterprise needs.

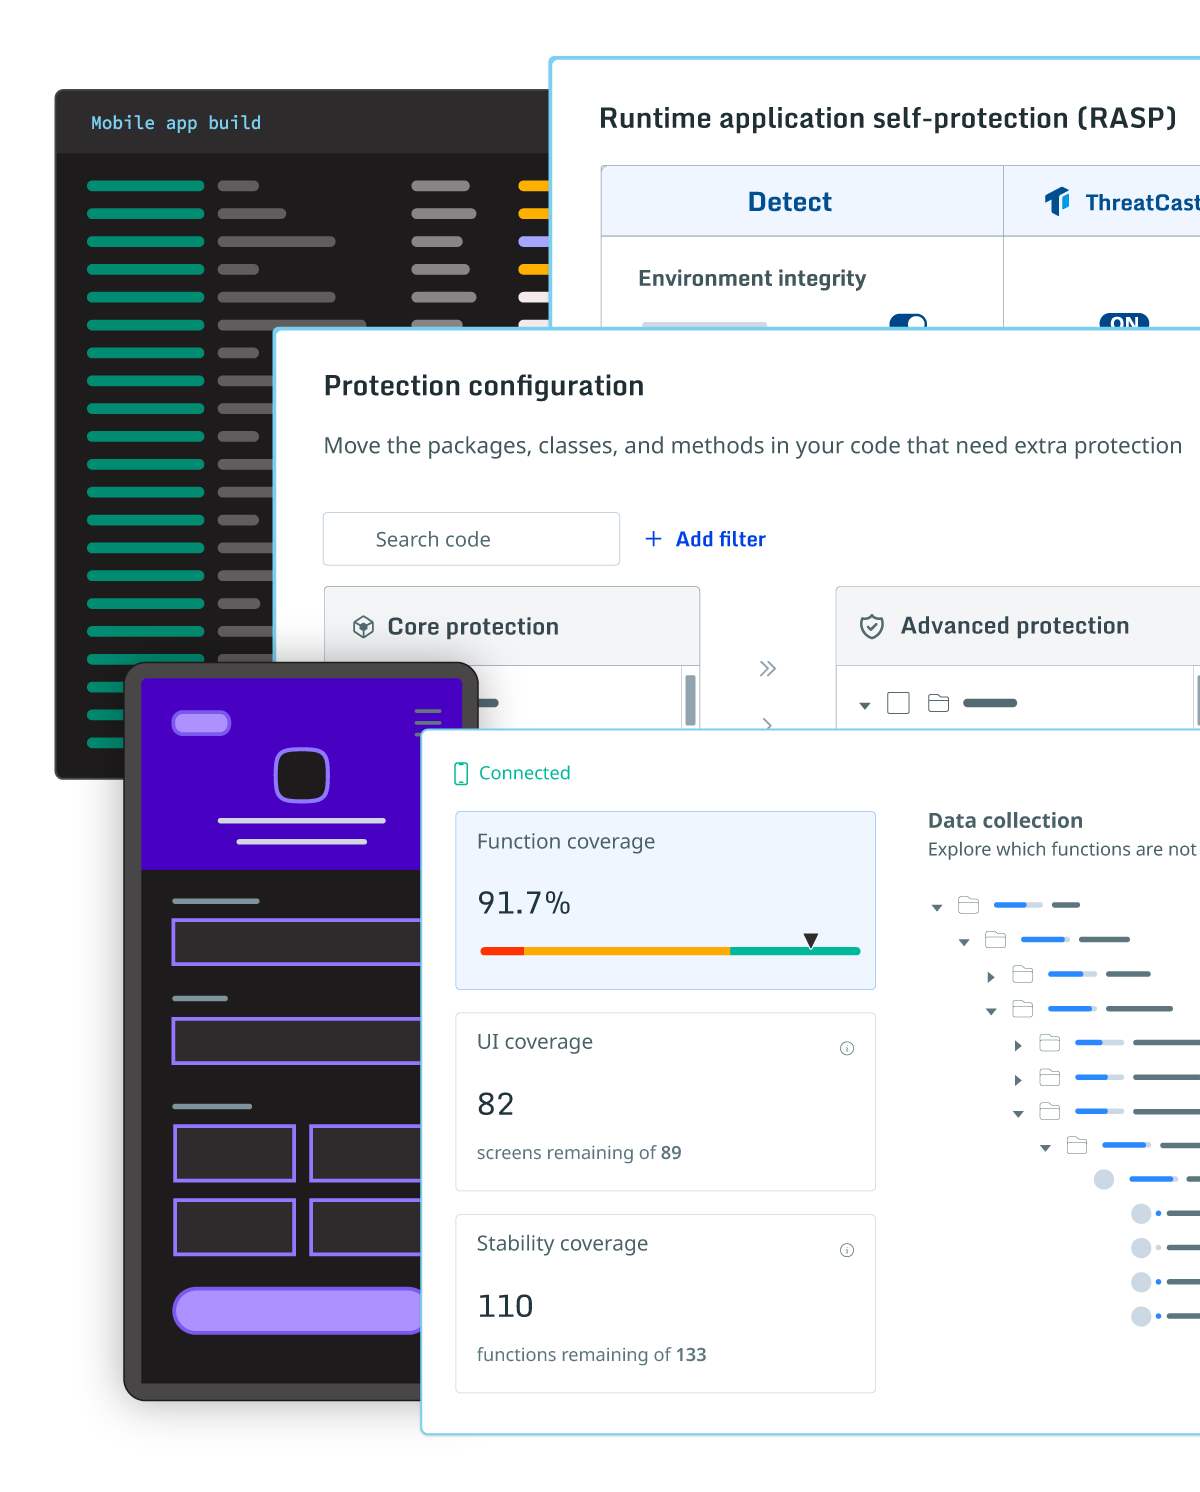
Threatcast THREAT MONITORING

Monitor threats to mobile apps & SDKs in real time, adapt security configurations & identify security gaps & vulnerabilities post-publication.

Explore malware protection resources

Malware on mobile phones poses the biggest risk to the device end users. Though detection and mitigation often falls in the technical purview of the platforms themselves (Android), specific mobile malware may take advantage of the knowledge gained during a reverse engineering effort to explicitly target and exploit apps on a user’s phone.

There is no single answer to protecting your app and your users data from malware, but having an in-depth defense strategy is the most effective way to prevent or limit the impact of malware on your application.

A dropper application is a common method used to install Android malware on mobile devices. (Other methods include phishing links and sideloading from third-party sources.)

Threat actors frequently disguise dropper apps on the Google Play Store as genuine apps (e.g., calculators, QR code scanners). When a user downloads and opens a dropper app, malware is secretly unpacked and loaded onto the device.

From there, the malware may exhibit other behaviors – such as downloading additional attack modules from a command and control (C&C) server, or trying to gain administrator privileges.

Malware may combine a variety of malicious techniques to exploit mobile applications. Some common examples include:

Accessibility (a11y) services are native features on the Android OS that assist users with disabilities. Malware can trick users into granting a11y privileges, which can then be used to interfere with a mobile app’s UI – such as keylogging sensitive account information.

Screen recording is a similar malware technique for stealing sensitive data. Screen-captured content (e.g., login credentials) is streamed to a C&C server by administrator commands from the admin panel.

UI injections typically happen in one of two ways to capture sensitive information or mislead the user. An unauthorized activity injection can be inserted above the legitimate app (e.g., a layer that mimics a login screen). Alternatively, an overlay injection inserts additional views or UI elements into the app.

Clipboard spying is when malware harvests and exfiltrates sensitive data that the device user copies to clipboard to paste later.

There are two key defensive considerations against mobile malware:

  1. Making data very hard to exfiltrate.
  2. Making any successfully stolen data very hard to reuse.

Making data hard to exfiltrate requires mobile app protections like runtime application self protection (RASP), which injects different security checks in the code, as well as real-time threat monitoring capabilities to detect malicious activities.

Making stolen data hard to reuse requires protections like device binding to counter manual reuse of stolen data. This means that the legitimate user’s application must be used on their specific mobile device in order to validate account access and any subsequent transactions. Device binding provides a safeguard against an attacker reusing credentials to login on a different device.

However, a bot with stolen credentials can automatically bypass client-side app protections by directly interacting with a mobile API. App attestation capabilities use token exchanges to ensure that only genuine mobile apps can call server APIs while blocking bots, scripts, agents, and non-genuine apps.

Guardsquare provides both the security expertise and customizable protection tools required to harden Android applications against malware attacks. Using DexGuard’s built-in malware protection feature, you can easily protect against accessibility services abuse, screen spying, and UI injection attacks while maintaining the full functionality and proper usability of your app for all users. By combining DexGuard’s malware protection with code hardening and runtime protection you can ensure the most robust protection.

You can learn more about malware, the common attack methods and behavior, and how to protect your app in our malware research at the Mobile Application Security Research Center.